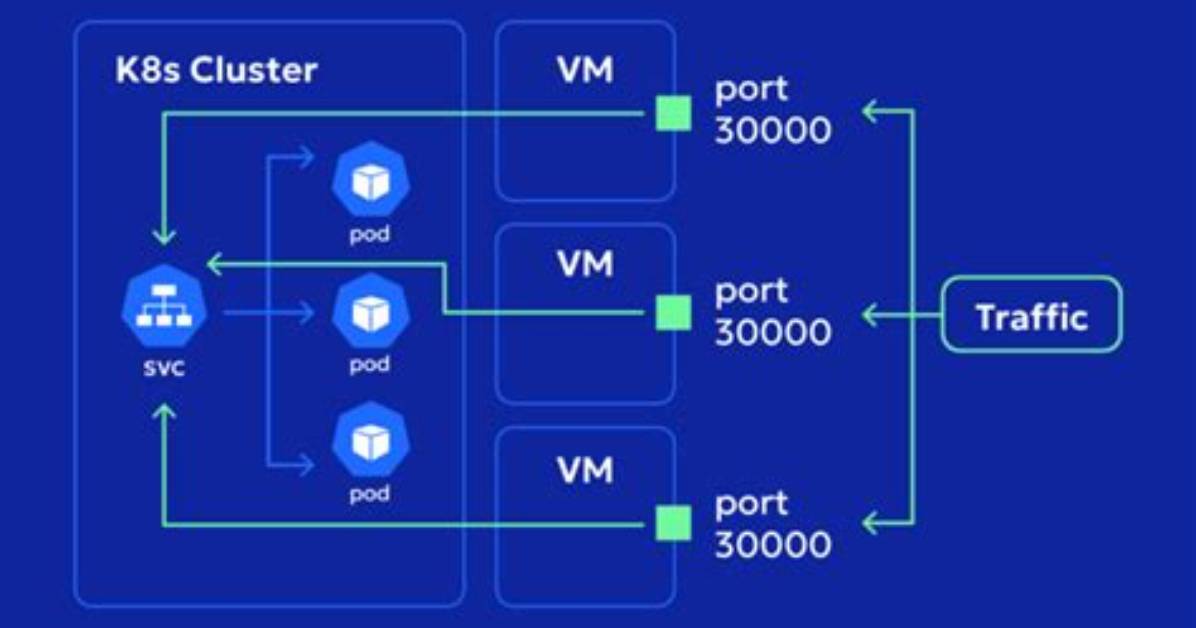
This section addresses frequently asked questions about NodePort Kubernetes, providing clear and informative answers to common concerns and misconceptions.
Question 1: What is NodePort in Kubernetes?
Answer: NodePort is a Kubernetes service type that exposes an application running on a cluster node to the external network. It allocates a port on each node, allowing external systems to access the service through that port.
Question 2: When should I use NodePort?
Answer: NodePort is suitable when you need to expose a service outside the Kubernetes cluster without using an external load balancer or ingress controller. It's commonly used for simple deployments or testing purposes.
Question 3: What are the limitations of NodePort?
Answer: NodePort has limited scalability compared to other service types like LoadBalancer or Ingress. Additionally, it exposes services directly to the internet, making security measures like TLS encryption crucial.
Question 4: How do I create a NodePort service in Kubernetes?
Answer: To create a NodePort service, use the kubectl command with the "--type=NodePort" option. Specify the port number and target port for your application, and Kubernetes will assign a port on each node.
Question 5: Can NodePort be used with multiple nodes?
Answer: Yes, NodePort can be used with multiple nodes. Each node in the cluster will have the service exposed on the specified port, providing load balancing across the nodes.
Question 6: How do I secure a NodePort service?
Answer: To secure a NodePort service, implement TLS encryption by adding a TLS secret to the service definition. This encrypts communication between external clients and the service, protecting data in transit.

